Whether you have any questions, or wish to get a quote for your project, or require further information about what we can offer you, please do not hesitate to contact us.
Contact us Need a reliable software development partner?
S3Corp. offers comprehensive software development outsourcing services ranging from software development to software verification and maintenance for a wide variety of industries and technologies



Software Development Center

Insights
Table Of Content
Key Takeaways
Introduction
What Is AI in Fintech?
Why Fintech Companies Are Adopting AI Now
What Are the Main Applications of AI in Fintech?
Which Fintech Applications Benefit Most From AI?
What Are The Business Benefits Of AI In Fintech?
What Are The Biggest Challenges And Risks Of Implementing AI In Fintech?
Who's Accountable When A Third-Party AI System Gets A Fintech Decision Wrong?
How Does Generative AI Fit Into Fintech?
How Do You Implement AI In A Fintech Product?
What AI Architecture And Technology Stack Does A Fintech Application Need?
How Should a Fintech Company Choose an AI Use Case First?
How Fintech Companies Implement These AI Use Cases
How To Evaluate an AI in Fintech Development Partner?
How Much Does It Cost to Implement AI in Fintech?
What Are the Future Trends in AI for Fintech?
AI In Fintech Vs Traditional Automation: When Should You Use AI?
AI in Fintech: Final Decision Checklist
How Can You Start An AI In Fintech Project?
FAQ
A practical guide to AI in fintech: where it creates the most value, the risks that matter, who stays accountable, and a step-by-step approach to implementation for engineering and product leaders.
16 Sep 2026
Fraud losses in digital payments keep climbing even as financial institutions add more rules to stop them. That gap between static, rule-based defenses and adaptive attackers is a big reason so many banks and fintechs now turn to AI in fintech to close it.
AI in fintech uses machine learning, generative AI, natural language processing, and related technologies to automate financial processes, detect fraud, assess risk, personalize customer experiences, and support faster decisions. The strongest implementations do not simply bolt on an AI feature. They connect one defined financial outcome to reliable data, the right model, human oversight, and security controls.
This guide sits inside the broader fintech software development resource by S3Corp. It will break down where AI creates real value in fintech, what changes once a model touches money and personal data, and how a team moves from a pilot to a production system that a regulator will actually accept. You will find a use-case matrix, a risk-and-control framework, a 7-step implementation roadmap, and the one accountability question every fintech and banking team needs to answer before writing a line of model code.
|
Use case |
Data you need to start |
Who stays accountable if it's wrong |
|
Fraud detection |
Real-time transaction stream |
The compliance and risk team |
|
Credit scoring / underwriting |
Historical repayment plus alternative data |
The credit risk officer |
|
Customer service / KYC |
Clean customer records |
The operations and compliance lead |
|
Compliance / RegTech |
Audit trail infrastructure |
The legal and compliance function |
AI in fintech is the application of artificial intelligence and machine learning to financial products, operations, risk management, customer service, and decision-making. Common applications include fraud detection, credit risk assessment, financial assistants, personalized financial management, and investment analytics. Unlike older rule-based automation, these systems learn from data and adapt as conditions change.
A simple way to think about it is a capability-to-function map:
The technology already powers credit scoring, fraud detection, algorithmic trading, portfolio management, regulatory compliance, and customer service.
The difference between older fintech automation and AI-enabled fintech comes down to how each system handles new, unstructured, or unexpected data.
|
Dimension |
Traditional automation |
AI-enabled fintech |
|
Logic |
Fixed rules and thresholds |
Learned patterns from historical and live data |
|
Fraud detection |
Flags known rule violations |
Detects unfamiliar anomalies across accounts and devices |
|
Credit decisions |
Static scorecards |
Continuous risk scoring from broader data signals |
|
Customer support |
Scripted FAQ bots |
Context-aware assistants using NLP |
|
Maintenance |
Manual rule updates |
Requires ongoing model monitoring and retraining |
AI adoption in fintech is speeding up because the tooling has matured and the payback is now measurable. Research and Markets estimates the global AI-in-fintech market at roughly $28.8 billion in 2025, projected to reach around $93.9 billion by 2032 at an 18.4% CAGR.
Market size estimates vary across research firms depending on scope and methodology, but the direction is consistent: sustained, double-digit growth. What matters more to a technical buyer is the return, not just the market size.
|
Metric |
Figure |
Source |
|
Global AI-in-fintech market, 2025 |
~$28.8 billion |
Research and Markets |
|
Projected market by 2032 |
~$93.9 billion (18.4% CAGR) |
Research and Markets |
|
Financial firms reporting 5%+ revenue increase from AI |
Nearly 70% |
|
|
Financial firms reporting 5%+ cost reduction from AI |
More than 60% |
NVIDIA |
Fraud and trading teams are not the only ones benefiting. NVIDIA's survey also found that trading and portfolio optimization lead generative AI ROI at 25% of responses, with customer experience close behind at 21%.
That spread across use cases is exactly why a single "AI strategy" rarely works. Each application needs its own data, risk profile, and delivery plan.
AI in fintech groups naturally by the financial workflow it supports:
|
Application area |
Representative use cases |
Typical AI capability |
Primary business goal |
|
Fraud and financial crime |
Transaction monitoring, alert scoring |
Anomaly detection |
Reduce losses, false positives |
|
Lending and underwriting |
Credit scoring, document review |
Predictive models, NLP |
Faster, more consistent decisions |
|
Wealth management |
Robo-advisory, rebalancing |
Portfolio algorithms |
Scalable, personalized advice |
|
Customer experience |
Virtual assistants, routing |
NLP, generative AI |
Faster resolution, lower cost |
|
Compliance and RegTech |
KYC checks, alert triage |
Document extraction, pattern matching |
Lower manual review load |
|
Operations |
Reconciliation, data entry |
Intelligent document processing |
Free up staff time |
|
Risk and forecasting |
Cash-flow prediction, portfolio risk |
Time-series ML |
Better planning, fewer surprises |
|
Trading and investment |
Signal generation, market analysis |
Pattern recognition |
Faster, data-backed decisions |
AI helps fintech companies detect unusual transactions and behavior by finding patterns across transaction, account, device, and customer data. Common applications include anomaly detection, transaction monitoring, alert prioritization, and fraud scoring.
Detection accuracy alone does not solve the problem, though. A production fraud system also needs reliable data, transaction rules, human review, sensible thresholds, explainability, monitoring, and controls for false positives and attack patterns that shift over time. Hence, model output can become part of a controlled security process rather than a standalone decision-maker.
A typical fraud-detection pipeline moves through seven steps:
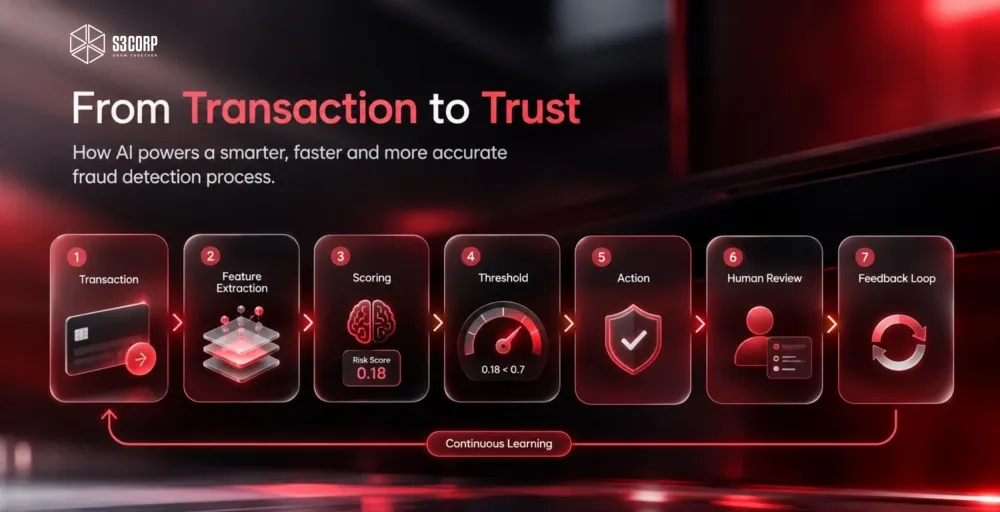
The US Department of the Treasury's report on managing AI-specific cybersecurity risks in financial services documents both sides of this coin. AI strengthens fraud defenses, but it also opens new attack surfaces, including adversarial attempts to manipulate the models themselves.
AI output typically works alongside rules, investigation workflows, authentication controls, and human review. A model does not replace that stack; it makes it faster and more precise. For a deeper technical breakdown, see AI fraud detection in financial services.
AI can analyze broader and more frequently updated data than traditional credit models, which helps lenders spot patterns tied to creditworthiness and default risk. The real implementation challenge is making sure model performance does not come at the cost of explainability, fairness, data governance, or regulatory accountability.
Traditional underwriting relied on a narrow credit history. AI-driven models now fold in alternative data — cash-flow patterns, utility payments, transaction history — to expand who qualifies for credit responsibly.
|
Stage |
Traditional workflow |
AI-assisted workflow |
|
Data inputs |
Credit bureau history, income |
Bureau data plus alternative data (cash flow, utility payments) |
|
Decision speed |
Days |
Minutes to hours |
|
Risk detection |
Static scorecards |
Continuously updated models |
|
Explainability |
Simple, rule-based logic |
Requires dedicated explainability tooling |
Before launch, most teams need a short controls checklist:
Teams evaluating a build for this space can see the fuller build process in the guide to lending platform development.
High-impact lending decisions still require validation, governance, and oversight, especially where fair-lending rules apply. Explainability matters here: a model that cannot show why it declined an applicant creates real regulatory exposure.
AI supports robo-advisory by analyzing investor risk preferences, portfolio data, and market information to generate recommendations. Fintech platforms use algorithms for portfolio allocation, personalization, and rebalancing support.
The level of automation depends on the product's risk controls and regulatory requirements, not on how advanced the model is. The typical workflow moves from investor profile, to risk assessment, to recommendation, to ongoing portfolio monitoring. See wealth management software development for the engineering side of this.
AI improves fintech customer service through virtual assistants, NLP, knowledge retrieval, and automated support workflows. These systems answer routine questions, retrieve account information, summarize cases, and route complex issues to a human agent.
Sensitive financial actions still need controlled authentication and authorization before an AI assistant can act on them.
|
Good fit for AI |
Needs human handoff |
|
Balance and transaction lookups |
Disputed charges, fraud claims |
|
Product FAQs and onboarding help |
Account closures, hardship requests |
|
Status updates on applications |
Complex loan restructuring |
AI assists compliance teams by processing documents, extracting information, identifying patterns, and prioritizing alerts for transaction monitoring. This can cut manual work significantly in selected workflows.
AI does not remove the need for documented controls, audit trails, and jurisdiction-specific regulatory requirements. Those stay with the compliance team. Explore KYC/AML solutions for fintech and RegTech compliance automation for implementation depth.
AI automates repetitive fintech operations such as document classification, data extraction, reconciliation support, and information retrieval. These applications are often easier to pilot than high-impact financial decision systems, since the AI assists an existing workflow rather than making the final call.
That lower-risk profile makes operations a common first AI project for teams that want a fast, low-drama win before tackling fraud or credit models.
Machine learning analyzes historical and current financial data to support forecasting and decision support. Financial teams apply these methods to cash-flow forecasting, customer behavior analysis, and portfolio risk.
Model quality depends heavily on data quality, changing market conditions, and ongoing validation. A forecasting model that was accurate last quarter can drift quietly if nobody monitors it.
AI supports trading and investment workflows through market-data analysis, pattern detection, signal generation, and decision support. These systems range from analytical tools for human investors to highly automated strategies.
The right level of automation, validation, and human control should match the financial and operational risk of the strategy, not the sophistication of the model.
AI is most valuable in fintech where large volumes of financial data, repetitive decisions, risk patterns that shift, or heavy customer-service demand create a measurable advantage. Fraud detection and credit risk are especially strong candidates. Customer support, personal finance, trading, and back-office operations offer real, if more incremental, gains.
|
Use case |
Primary AI technique |
Typical business outcome |
|
Fraud detection and prevention |
Anomaly detection, deep learning |
Lower fraud-loss rate |
|
Credit scoring and risk assessment |
Predictive models, alternative data |
Faster, fairer approvals |
|
Customer service and AI assistants |
NLP, generative AI |
Lower cost per contact |
|
Personal finance and recommendations |
Predictive analytics |
Higher engagement |
|
Algorithmic trading and portfolio management |
Reinforcement learning |
Faster, more consistent execution |
|
AML/KYC and transaction monitoring |
Pattern and network analysis |
Faster clean-case onboarding |
|
Document processing and underwriting |
Computer vision, NLP |
Shorter cycle time |
|
Forecasting and financial operations |
Time-series models |
Better cash-flow visibility |
Teams building or refreshing a mobile banking app often start here, since fraud alerts and personalization sit directly in the customer-facing layer.
The business case for AI in fintech rests on measurable gains in risk detection, operational efficiency, customer experience, decision speed, and personalization. Value is strongest when a team ties every use case to one defined KPI, not to model accuracy alone. The goal is optimizing cost and performance together, not chasing the highest accuracy score in isolation.
|
Business area |
AI use case |
KPI to track |
|
Fraud |
Anomaly detection |
Fraud-loss rate, false-positive rate |
|
Lending |
Credit scoring |
Approval time, default-prediction accuracy |
|
Support |
AI assistants |
Resolution time, containment rate |
|
Operations |
Document and process automation |
Processing time, manual workload |
|
Personalization |
Recommendation engines |
Engagement, conversion |
IBM's own research points to the same pattern. Institutions see the strongest return when AI reduces manual error and streamlines one specific, measurable workflow. General-purpose deployment, without a named workflow behind it, rarely produces the same result. That is also why so much of the coverage of AI finance companies focuses on named use cases instead of broad promises: the specificity is where the ROI actually lives.
The hardest part of fintech AI is usually not choosing a model. It is governing that model inside a regulated, data-sensitive environment, where privacy, bias, explainability, security, and compliance failures all carry real financial and legal consequences.
|
Risk |
Why it matters in fintech |
Engineering control |
Human oversight |
|
Data privacy |
Sensitive financial and personal data |
Encryption, access control, data minimization, synthetic data generation |
Privacy review before launch |
|
Algorithmic bias |
Can produce discriminatory lending outcomes |
Bias testing across protected groups |
Fairness sign-off by a risk officer |
|
Lack of explainability |
Regulators require reasons, not just outputs |
Explainable AI tooling, model documentation |
Compliance review of decision logic |
|
Security exposure |
Fraud models are high-value attack targets |
Secure architecture, ISO-aligned controls |
Incident-response ownership |
|
Regulatory compliance |
Rules vary by market and shift often |
Automated compliance monitoring |
Legal review of new use cases |
|
Model drift |
Live models decay as behavior changes |
Continuous monitoring, scheduled retraining |
Periodic model-risk review |
Synthetic data generation is one of the more practical additions to that control list for 2026 builds. Training a credit-scoring model on synthetic financial histories — data engineered to mirror real repayment patterns without containing any actual customer PII — sidesteps a large share of the privacy review a live dataset would trigger, while still producing a training set that behaves statistically like the real thing.
An ISO 27001-certified delivery process addresses several of these rows by design. Access management, data handling, and incident response are already part of a certified management system, not something a project team improvises under deadline pressure.
Most companies are increasingly pairing that expectation with ISO 42001, the newer international standard for AI management systems (AIMS): where ISO 27001 governs information security, ISO 42001 governs how an organization manages AI risk, oversight, and lifecycle governance specifically. It's quickly becoming the reference point procurement teams reach for when evaluating an AI delivery partner, alongside the security guarantees ISO 27001 already covers.
Teams mapping this against a specific standard can go deeper in the guides to PCI DSS compliance for payment data, and RegTech compliance automation for the regulatory-reporting side of the same problem.
When a bank or fintech uses AI, the regulator holds the financial institution accountable for the outcome, regardless of who built the model. The EU AI Act's high-risk rules for credit scoring, US model-risk-management expectations, and the Monetary Authority of Singapore's FEAT principles all point the same direction: a company can outsource the build, but it cannot outsource the liability.
|
Requirement |
What it means, conceptually |
Framework driving it |
|
Explainability / audit trail |
A record of how a model reached a decision, not just the decision itself |
EU AI Act, Annex III (high-risk credit scoring) |
|
Bias testing evidence |
A documented testing method, not a fairness claim alone |
MAS FEAT Principles (Singapore) |
|
Data residency and handling |
Where training and inference data lives, and how it is isolated |
GDPR and market-specific data rules |
|
Component transparency |
An inventory of the models, training data, and third-party or open-source components inside the system |
Emerging 2026 procurement standard, often requested as an AI Bill of Materials (AI-BOM) |
|
Third-party vendor oversight |
An ongoing, regulator-facing register of every ICT and AI vendor relationship, not a one-time vendor form |
DORA (EU, in force since January 2025) |
|
Change-notification process |
Notice before retraining or changing a live model |
An emerging supervisory expectation |
Under Annex III of the EU AI Act, systems used to evaluate a person's creditworthiness or set a credit score are classified as high-risk. That classification brings documentation, human-oversight, and bias-testing duties with it. Fraud detection is the one named exception.
Timeline update: the EU's Digital Omnibus on AI (Regulation 2026/1744), in force since July 2026, pushed the compliance deadline for these Annex III obligations from August 2026 to December 2, 2027. The high-risk classification itself has not changed, and a detailed breakdown of what moved and what didn't is worth a read before assuming the extra runway means the requirement went away. Only the clock moved.
The Monetary Authority of Singapore takes a similar stance through its FEAT principles, first published in 2018. They set out expectations for fairness, ethics, accountability, and transparency in how financial firms use AI and data analytics.
A fourth framework belongs in this conversation, because it targets the vendor relationship directly rather than the AI decision itself. The EU's Digital Operational Resilience Act, known as DORA, has applied to banks, insurers, and other financial entities since January 2025. It requires financial institutions to keep a Register of Information covering every ICT third-party arrangement — AI vendors included — and to keep that register current for their regulator, not just fill it out once during procurement. DORA doesn't replace the AI-specific rules above. It sits alongside them, aimed squarely at the vendor relationship, and it reinforces the same point from a different angle: ongoing third-party oversight is now a regulatory obligation, not a one-time vendor-selection checkbox.
That oversight starts with a simple, concrete question: can the vendor produce an AI-BOM? An AI Bill of Materials lists the models, training data sources, and open-source or third-party AI components inside a system, the same way a software bill of materials lists code dependencies. Without it, a compliance team is taking a vendor's word for what's actually running in production. With it, data lineage and dependency tracking become something a regulator can actually audit.
This is exactly where an ISO 27001-certified delivery process earns its place in the conversation, not as a sales pitch, but as a concrete answer to the accountability question above. Security and IP protection get built into an engagement from day one, which matters because the institution stays on the hook for the outcome no matter which partner wrote the code.
Generative AI works best in fintech when it operates on controlled enterprise data inside clearly bounded workflows. Financial assistants, document summarization, knowledge retrieval, customer support, and analyst assistance are common examples. High-assurance financial decisions need stronger validation and governance than ordinary content-generation use cases do.
|
Risk tier |
Example use cases |
Governance needed |
|
Lower risk |
Internal knowledge search, summarization, drafting |
Standard review |
|
Medium risk |
Customer support, document workflows, analyst assistance |
Human review, monitoring |
|
Higher risk |
Credit decisions, investment recommendations, autonomous transactions |
Full model governance, audit trail, regulatory sign-off |
Treasury's own review flags the core problem with pushing generative AI into the higher-risk tier: outputs are probabilistic rather than deterministic, which makes them genuinely hard to validate for high-assurance financial decisions.
Semantic guardrails are the engineering answer most teams reach for first. A guardrail sits between the model and the customer as a separate, deterministic layer. It checks each output against a fixed set of rules before anything ships. Done well, it blocks an out-of-scope prompt, catches a hallucinated interest rate or account balance, and stops a support assistant from generating anything that reads as investment advice it was never licensed to give. The guardrail itself doesn't reason probabilistically — that's exactly why it works as a backstop for a model that does.
That gap is also why most production agentic AI deployments in finance today still keep a human in the approval loop for anything above the medium-risk tier.
Public LLM APIs are not automatically suitable for sensitive financial data. Data handling, access control, retention, and deployment architecture need assessment for each specific use case before anything sensitive touches the model.
Employee assistants, customer-facing chat, document generation, and bounded workflow agents fall across that spectrum. Explore AI integration services and agentic AI for how these systems get built responsibly.
A practical fintech AI implementation starts with a measurable business problem, then moves through data assessment, use-case selection, model strategy, integration, security and compliance controls, testing, deployment, and continuous monitoring. The goal is not to launch the most advanced model available. It is to deploy the smallest reliable AI capability that produces a measurable outcome.
Fintech teams that need engineering, QA and testing, DevOps, or ongoing maintenance support for this kind of roadmap often bring in a delivery partner for exactly this stretch of the process. That need is one reason software outsourcing services and different collaboration models exist as distinct options, not a single fixed engagement type.
For over 19 years, S3Corp has delivered software for clients across banking, payments, and other regulated industries. Technical teams bring direct experience in fraud detection, compliance automation, and mobile banking builds. Services by S3Corp cover the full build-test-deploy cycle rather than a single slice of it — security, QA, and DevOps move in step with the model itself, instead of catching up to it later.
Dedicated fintech testing and QA and DevOps services cover steps 5 through 7 in particular, since model monitoring and release discipline tend to get underfunded once a pilot proves out.
A production fintech AI system typically combines application and API layers with governed financial data, model services, monitoring, security controls, and human-review workflows. Pick the architecture based on the use case and risk level, not around a preferred AI model or framework.
A scalable architecture built this way keeps pace as transaction volume grows, instead of forcing a rebuild every time usage doubles. Systems built around open banking architecture add another layer of complexity, since third-party data access needs its own governance on top of the model layer. Teams connecting several of these layers for the first time can see the pattern laid out in the guide to AI integration, which covers how the pieces talk to each other beyond just the model.
Use the NIST Cybersecurity Framework 2.0 for cybersecurity risk-management framing, and PCI DSS wherever payment-card data enters the picture. Teams often need R&D and DevOps capacity to build this layer correctly the first time, since retrofitting security and monitoring into a live AI system costs far more than designing for it up front.
The best first AI use case is not necessarily the most visible one. A strategic approach scores candidate projects across four filters: business impact, data readiness, implementation complexity, and regulatory or operational risk. Start with the option that scores well on impact without the heaviest compliance burden.
Fraud detection, document processing, customer support, and internal workflow automation can all be scored against the same simple checklist before a company commits engineering resources.
5-factor scoring checklist
Before comparing AI fintech companies or evaluation frameworks from outside vendors, score the candidate use case internally first. A lower-risk workflow with strong data and a clear ROI story is almost always a better first deployment. That holds true even against a high-risk, autonomous decision system with an impressive vendor demo.
Teams that skip this scoring step tend to pick the most exciting use case instead of the most winnable one, which is how AI pilots stall for a year without shipping.
Start with a business problem, not a model. A good first AI use case has a clear workflow, accessible data, measurable outcomes, manageable risk, and a defined human fallback.
Fintech teams generally implement AI one of three ways: building in-house with internal data science talent, buying an off-the-shelf AI-powered tool, or partnering with an outsourced development team to build something custom. Each path trades off speed, cost, and control differently.
Building in-house gives full control over the model and roadmap, but it requires hiring data science and ML engineering talent, which stays scarce and expensive in most markets. It works best for companies where AI is the core product, not a supporting feature.
Buying an off-the-shelf tool gets a team moving fast with a proven product, though it limits customization and can create long-term vendor lock-in. It suits narrow, well-defined problems like basic chat support or standard fraud-scoring add-ons.
Partnering with an outsourced engineering team blends speed with customization: the partner brings the delivery capacity and technical breadth, while your team keeps ownership of the product and data. S3Corp positions itself as a long-term delivery partner rather than a short-term staffing vendor, with security and IP practices built into how projects run day to day. Related: software outsourcing services and IT staff augmentation.
A fintech AI partner should be evaluated on more than its ability to build a model. A technical buyer should assess financial-domain understanding, data handling, architecture, security, testing, and what happens when an AI output turns out to be wrong.
That last question separates serious partners from vendors who have never operated an AI system in production. Save this list and bring it to your first vendor call.
16-question vendor due-diligence checklist
Use-case and product understanding
Data and model governance
Security and privacy
Architecture and integrations
QA and validation
Monitoring and operations
IP, ownership, and delivery model
AI in fintech has no single reliable price, because implementation effort depends on the use case, data condition, integration scope, and testing depth. A fraud model, an internal AI assistant, and a customer-facing financial assistant can require very different levels of engineering effort.
Rather than quote a number that will not match your project, it helps more to know what actually drives the cost.
|
Cost driver |
Why it varies |
|
Data preparation and quality |
Messy or siloed data adds significant prep time |
|
Model development or integration |
Custom models cost more than API-based ones |
|
Application and API integration |
Legacy core systems raise integration effort |
|
Security and access controls |
Regulated data needs stronger controls |
|
Testing and validation |
Financial decisions demand deeper QA cycles |
|
Cloud and model operating costs |
Usage-based, scales with transaction volume |
|
Monitoring and maintenance |
Ongoing, not a one-time cost |
|
Compliance and governance work |
Varies heavily by jurisdiction |
For a full breakdown of factors, see fintech app development cost.
The next phase of fintech AI moves beyond isolated prediction models and chatbots. It heads toward AI agents, workflow automation, and more deeply integrated decision-support systems. As autonomy increases, so does the need for validation, governance, security, and clear limits on what AI can decide without a person involved.
|
Trend |
Likely application |
Engineering implication |
Risk to monitor |
|
Agentic AI for bounded workflows |
Alert triage, reconciliation |
Needs strict permission scopes |
Uncontrolled autonomous actions |
|
AI-assisted fraud and cybersecurity |
Real-time transaction defense |
Requires low-latency infrastructure |
False positives at scale |
|
Intelligent reconciliation |
Back-office automation |
Structured data pipelines |
Silent data errors |
|
AI-assisted compliance |
Reporting, alert prioritization |
Auditable decision logs |
Regulatory misalignment |
|
Smaller, task-specific models |
Focused workflows over general chat |
Lower cost, easier to govern |
Model sprawl if unmanaged |
|
Financial assistants |
Employee and customer support |
Access-controlled retrieval |
Data leakage across sessions |
Agentic AI deserves a caution here: framing agents as autonomous decision-makers overstates where the technology stands today. In financial workflows, the safer framing is bounded workflow support, with permissions, logging, and human escalation built in from day one.
Teams tracking this shift can follow the broader pattern in the roundup of fintech trends and the deeper explainer on types of agentic AI, which breaks down how much autonomy each agent pattern actually carries.
Traditional automation works best when rules stay stable and predictable. AI earns its added complexity when a system must recognize patterns, make probabilistic predictions, process unstructured information, or adapt as behavior shifts. The real question is not whether a team can use AI. It is whether AI meaningfully improves a specific decision or workflow.
This decision tree also explains why so much legacy fintech infrastructure still runs on deterministic rules for core ledger and settlement logic. AI gets layered on top instead, for fraud scoring, personalization, and support. Migrating older systems to support that layered approach is its own project, covered separately in the guide to legacy system modernization.
Before starting an AI fintech project, confirm the business problem, the financial workflow, the data sources, the risk level, and the operating model. The goal is an AI use case that delivers measurable value while keeping financial, security, and operational risk under control.
Start with one measurable financial or operational problem, not an AI technology. Assess the data available, define the risk level and success metrics, pick the simplest model that meets the bar, build in security and human-oversight controls, and validate the pilot before expanding it further.
A short recap before moving forward:
For over 19 years, S3Corp has worked with clients across the tech sector in the US, UK, Singapore, and beyond. Projects have spanned banking, payments, and other regulated industries. Backed by an ISO 27001-certified delivery process and overseas talent experienced in fraud detection, compliance automation, and mobile banking, S3Corp builds innovative solutions around one constraint that never moves: the institution stays accountable, so the engineering has to hold up under audit. Each engagement runs as a co-creative partnership rather than a fixed handoff. Contact the S3Corp team to talk through a fintech AI use case, an architecture question, or an implementation roadmap. The goal of that first conversation is technical clarity, not a sales pitch.
AI in fintech is the use of technologies such as machine learning, natural language processing, predictive analytics, and generative AI to improve financial products and operations. Common applications include fraud detection, credit risk assessment, customer service, personal finance, investment analysis, and workflow automation.
AI identifies fraud, assesses credit risk, automates customer support, personalizes financial services, processes documents, forecasts outcomes, and supports investment decisions. The highest-value applications generally combine large datasets with repetitive, complex, or pattern-based financial decisions that a human would otherwise process by hand.
AI analyzes transaction and behavioral patterns to spot anomalies and potential fraud or cyber threats in real time. In production, it needs security controls, monitoring, human review, and governance around it, since false positives, attack patterns that shift, and model risk can all affect financial operations.
Agentic AI can coordinate multiple steps in a fraud workflow — gathering signals, prioritizing cases, requesting more information, and routing alerts. Because financial actions carry real consequences, these workflows need bounded permissions, an audit trail, validation, and a human escalation path rather than open-ended autonomy.
AI can be used securely in fintech, but security depends on the surrounding architecture, data controls, model governance, and monitoring built around it. Financial teams also need to manage privacy, bias, explainability, third-party exposure, and regulatory requirements rather than treating the model as a stand-alone component.
The main challenges include data quality, privacy, cybersecurity, model bias, explainability, regulatory compliance, integration with legacy systems, and ongoing monitoring. Generative AI adds extra concerns around unreliable outputs and the difficulty of validating a model for high-assurance financial decisions.
Evaluate a partner on how well they connect the AI use case to secure data handling, architecture, testing, and long-term support, not just their AI demos. Ask for evidence of relevant engineering work, security certifications, and clear responsibility for AI output failures.